Government and institutions
Model release evidence a reviewer can read.
Which model was approved, for which system, and what that system reports running.
Why it matters
Oversight runs on records.
Systems built by suppliers
Model updates arrive from outside the institution.
An unapproved release is a security event
For the institution responsible for the system.
Readable by someone outside engineering
Including what could not be confirmed.
How Vraelis Contour would apply
How Vraelis Contour worksFive steps, release to record.
Identify the release
Bind approval to the release and destination
Destination-bound approval covers that system and no more.
Integrate with a supported runtime
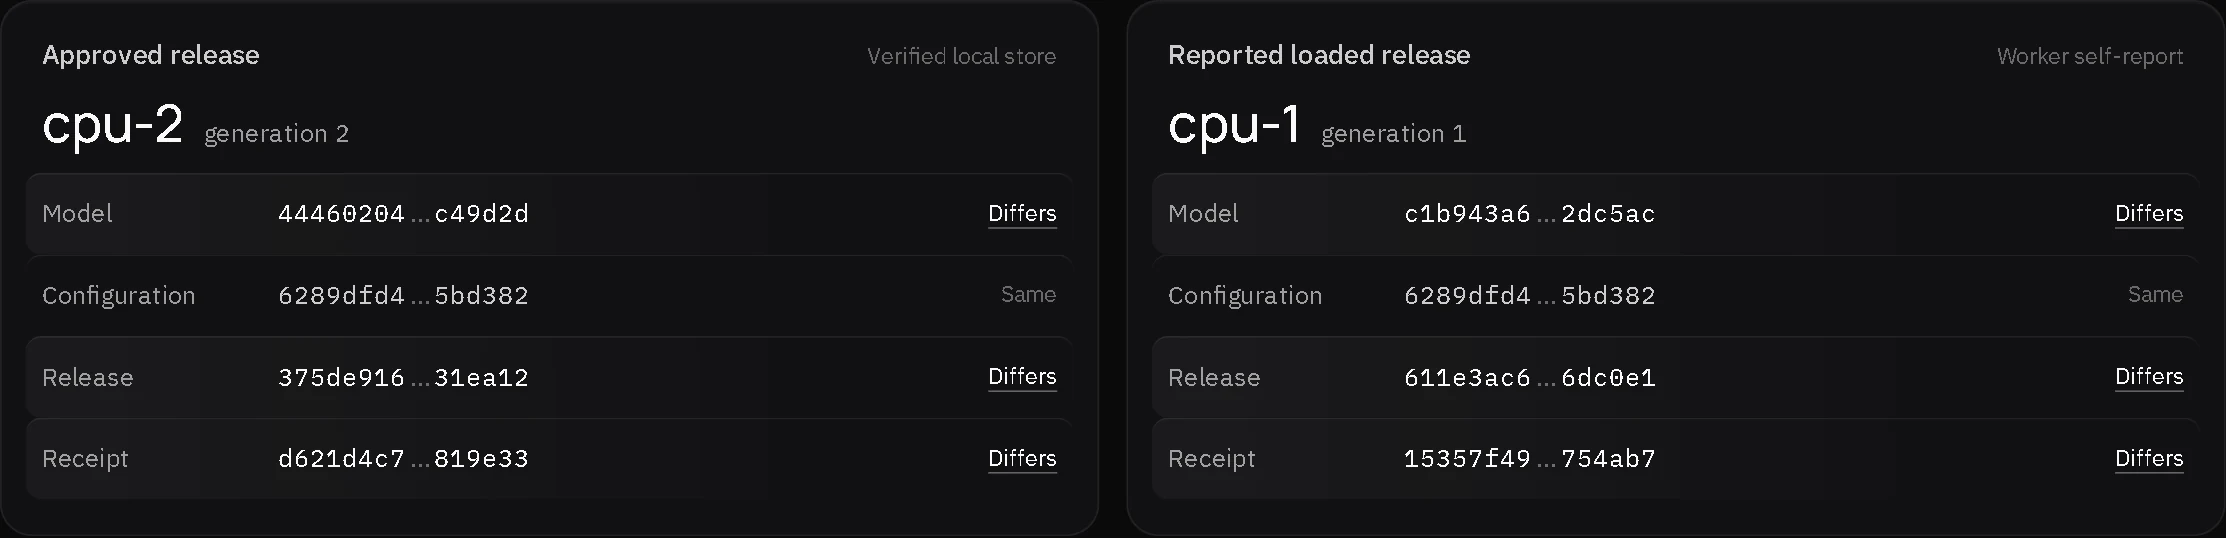
Compare approved and reported
Version mismatch shown as reload pending, in a view a reviewer can follow.
Preserve discrepancies, missing evidence and recovery
Limits
What we do not claim.
- No government deployments, contracts or customers.
- No procurement status, and no authorization to operate.
- No access to classified or restricted environments.
- No certification or regulatory compliance.
- No hardware attestation. Runtime identity is a worker self-report.
Related research
Release evidence a reviewer can read.
Join us in building it for government and institutional review.