Suppliers and integrators
For teams who ship models into systems they do not own.
Release, platform and security engineers at suppliers and system integrators.
Why it matters
You ship it. Someone else runs it.
The release lands in their system
Your signature does not grant permission to change it.
A wrong release is a security event
For both sides, even when nobody intended harm.
Both sides need the same record
Not a deployment log only one of you sees.
HypothesisThese teams meet this problem first. We are testing it.
How Vraelis Contour would apply
How Vraelis Contour worksFive steps, release to record.
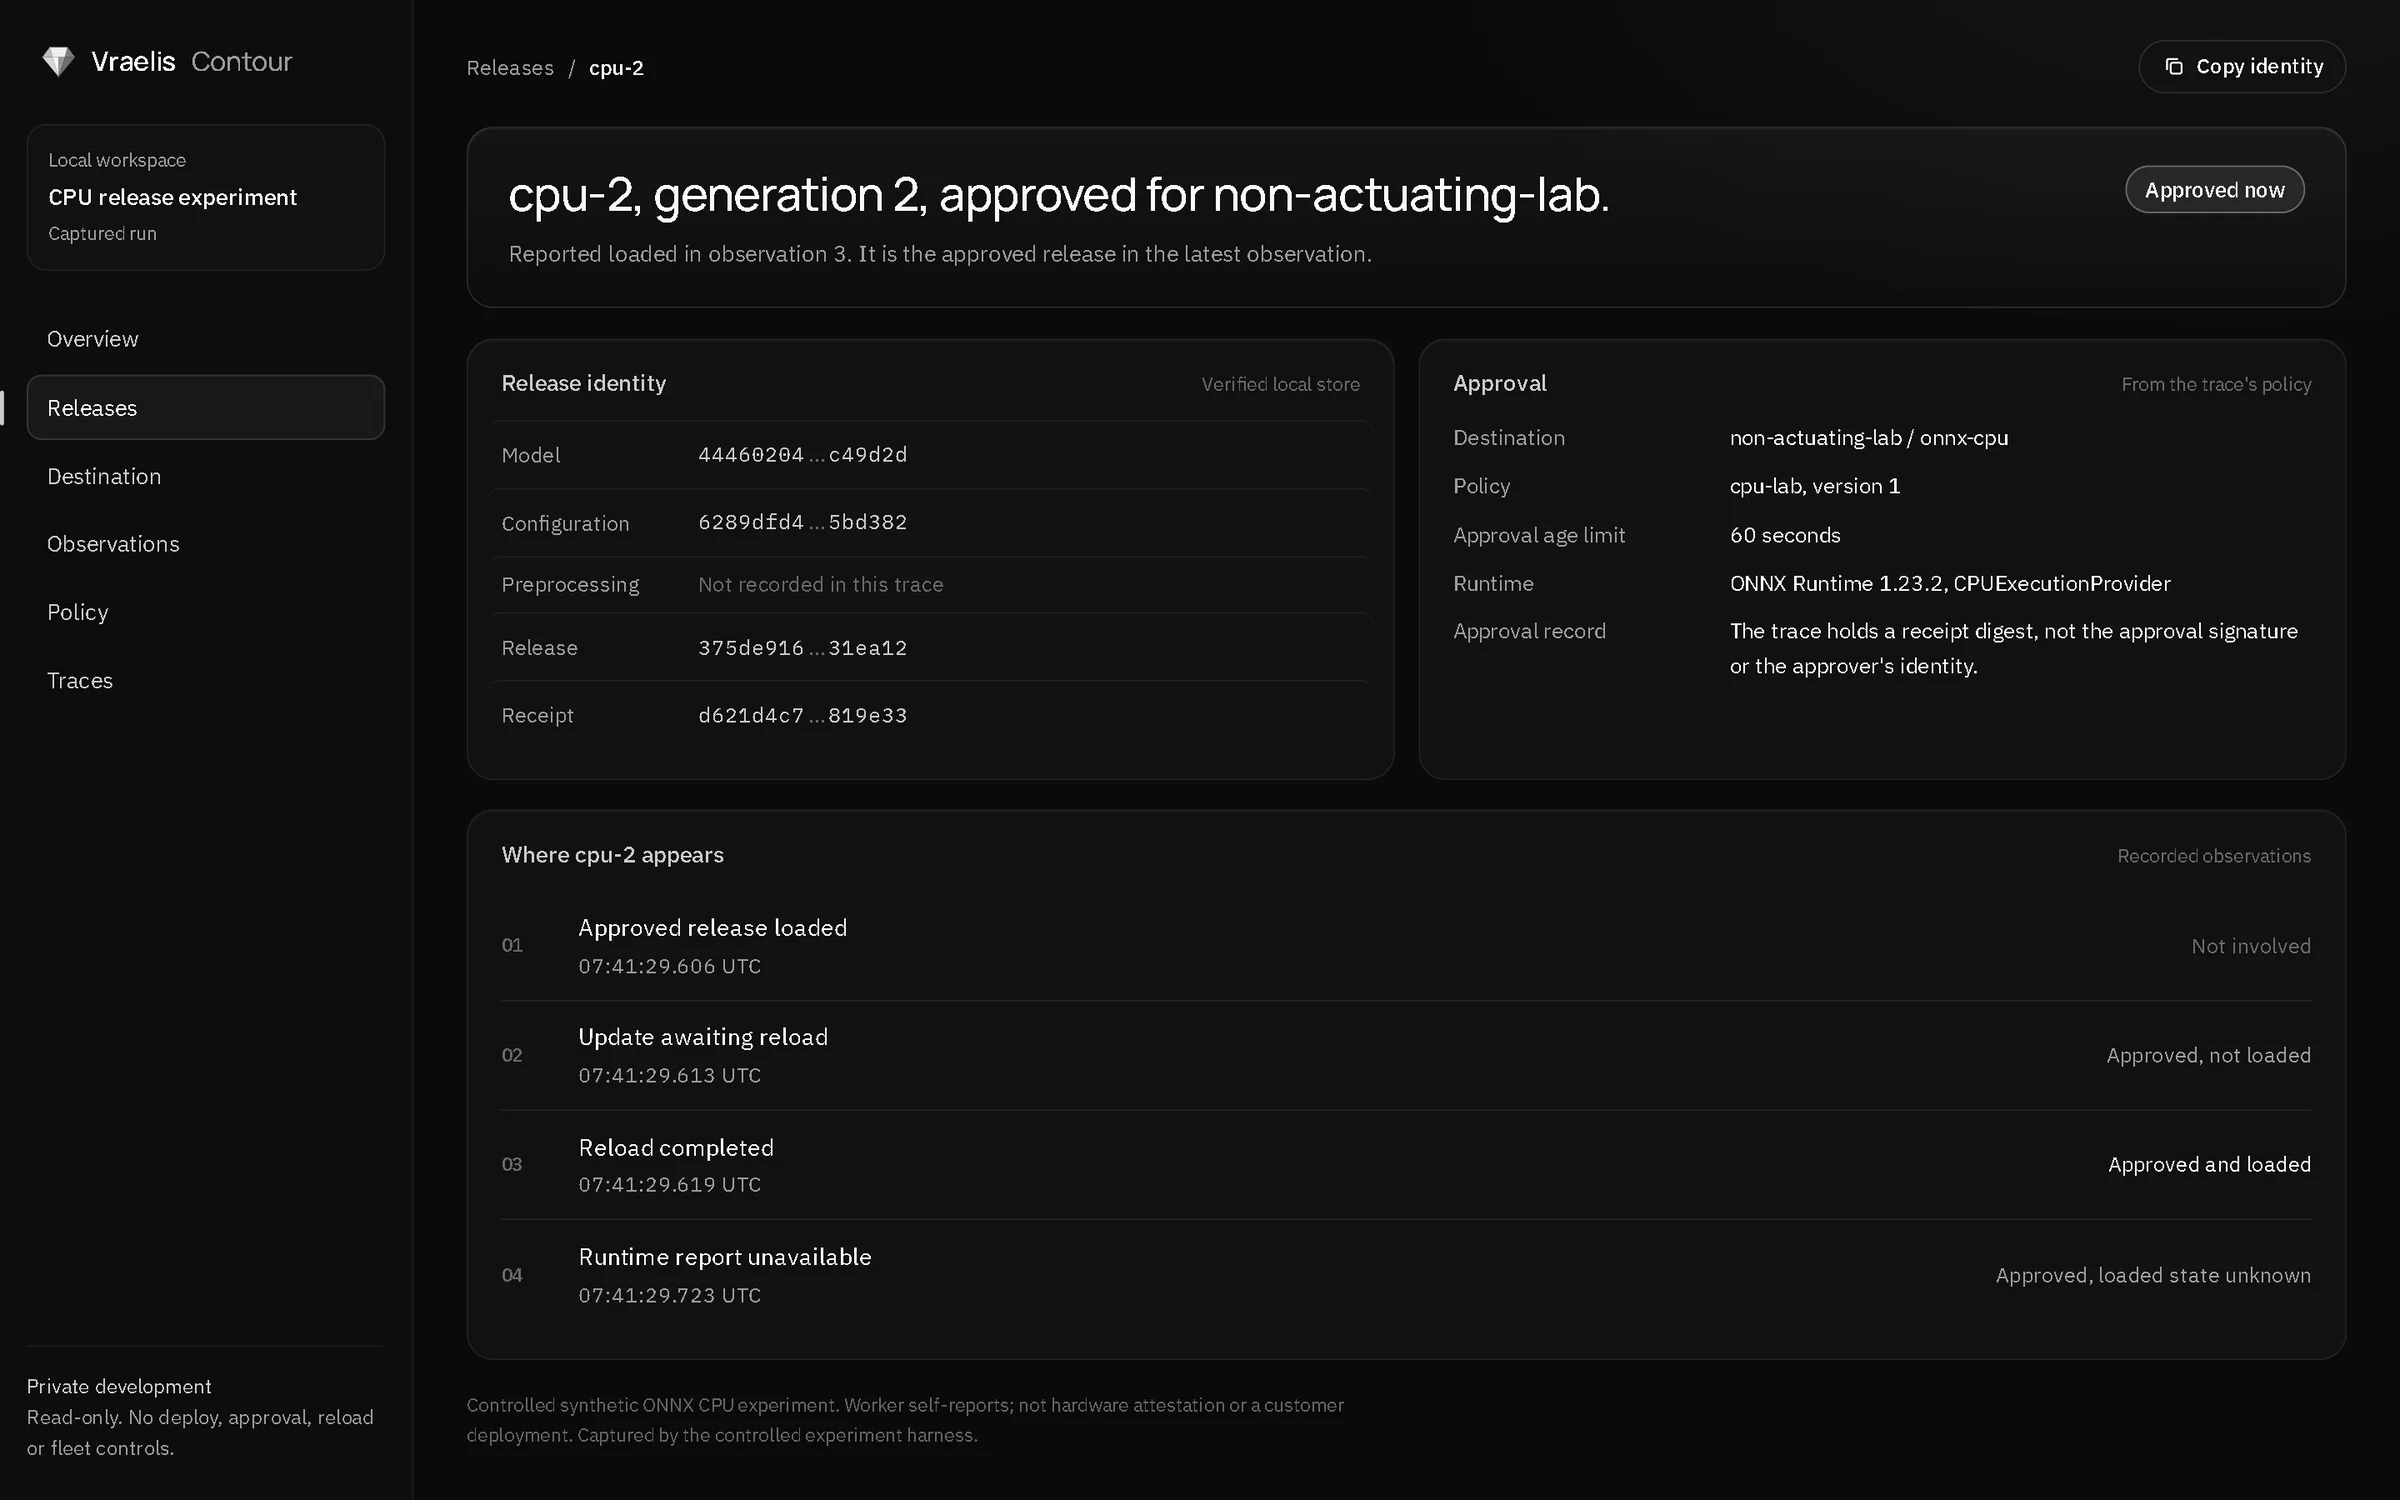
Identify the release
Bind approval to the release and destination
Release authorization may need two approvals: the supplier's and the operator's.
Integrate with a supported runtime
Compare approved and reported
Preserve discrepancies, missing evidence and recovery
Both sides start from the same deployment evidence.
Limits
What we do not claim.
- No customers or deployments, and no partner endorsement of Vraelis Contour.
- No pricing or general availability. Not for public use.
- No certification.
- No hardware attestation. Runtime identity is a worker self-report.
Related research
Build stronger evidence for model releases.
Join us in building Vraelis Contour.